There's a lab in Switzerland where they're building computers out of living human neurons. Sounds completely barking mad, right? Here's the thing: these brain cells compute using one million times less energy than silicon. Meanwhile, training a single AI model now produces the carbon emissions of 500 cars over their entire lifetimes. Microsoft, Google, and Amazon just committed billions to restart nuclear power plants because they can't keep the lights on. And your business? You're paying for ev
Why do smart people keep making the same catastrophic mistake? Cut security spending, congratulate themselves on efficiency, watch everything fall apart, spend vastly more recovering. It's not ignorance. It's psychology. Measurable costs are visible, politically defensible, easy to justify cutting. Invisible value is theoretical until it disappears. CFOs get promoted for cutting £50,000 from budgets. Nobody gets promoted for preventing breaches that don't happen. This asymmetry creates systemati
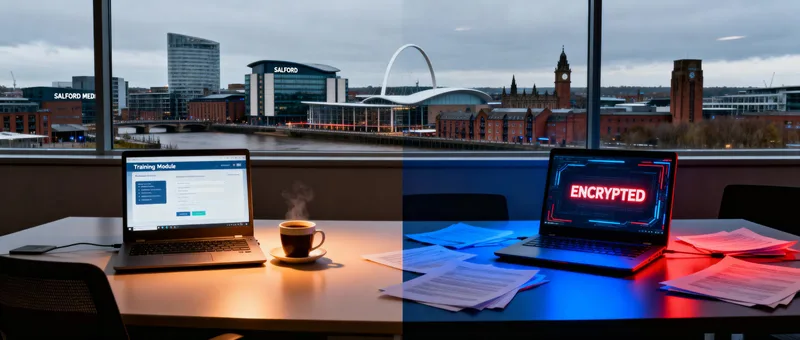
Manchester marketing agency, 28 staff, £2.4M revenue. CFO proposed cutting security training: "£12,000 annually for slides nobody watches." Board agreed. Six months later, junior account manager clicked phishing link in fake client brief. No training meant she didn't recognise warning signs. Credentials stolen, ransomware deployed, three weeks offline. Recovery costs: £190,000. ICO investigation: inadequate training documented. They saved £12,000 and spent £190,000 learning what training actuall
Stop cutting security costs based on gut feel and budget pressure. Start using actual frameworks that calculate downside risk. This practical guide walks you through evaluating any security spending decision: What's the notional function versus actual value? What's the cost of being wrong? What's the expected cost multiplied by probability? What invisible value disappears when you cut this? Includes checklists, decision trees, and real cost calculations for training, MFA, insurance, IT staff, an
The British Library decided not to implement MFA on administrator accounts. Their reasoning: "practicality, cost and impact on ongoing programmes." That decision cost them £7 million in recovery, 600GB of staff data dumped on the dark web, and over a year of service disruption. This is Mauven's Take on one of the clearest examples of the doorman fallacy in UK history. When cost-cutting decisions focus narrowly on immediate expense whilst ignoring catastrophic downside risk, you get exactly this
I've watched businesses make the same catastrophic mistake for 40 years. They look at security costs through a narrow efficiency lens, define roles by their obvious function, cut them to save money, and completely miss the invisible value. Until it's gone. Then they spend 10 times more fixing what they broke. The doorman fallacy explains every stupid IT decision I've ever seen: training cuts that cost millions in breaches, MFA removal that gifts credentials to attackers, insurance cancellation t
What's the most expensive cost-saving decision you can make? Firing your hotel doorman and replacing him with an automatic door. Saves you £35,000 a year in salary, costs you £200,000 in lost revenue because your hotel just became ordinary. This isn't about hotels. It's about every IT budget cut I've seen in the last 40 years. New episode drops today: The Doorman Fallacy, or How to Accidentally Destroy Your Business Whilst Congratulating Yourself on Efficiency Gains. Featuring examples that will
All right folks, buckle in. Last Monday, the planet just got schooled yet again in why we've put all our digital eggs in one totally cracked basket. AWS US-EAST-1 region had a DNS hiccup and half the world's internet decided it was nap time. Snapchat, Venmo, even the app that tells you if your cat's used the loo, all snuffed out. Why does a digital sneeze in Virginia take out customer payments in Edinburgh? And here's the kicker: this is the third major outage in five years for the same bloody r
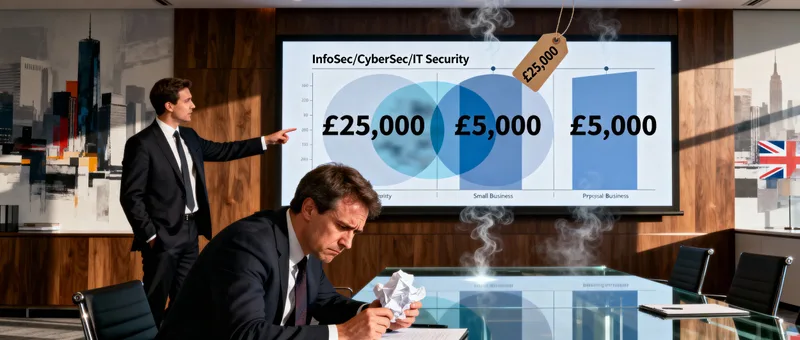
Security vendors are playing you for fools, and they're getting rich doing it. Every week I watch UK business owners waste £20,000 on "comprehensive cybersecurity platforms" when they needed £5,000 of basic IT security. The industry deliberately muddies the difference between InfoSec, CyberSec, and IT Security because confused customers pay premium prices for inappropriate solutions. Meanwhile, 50% of small businesses were breached in 2025, proving that expensive confusion doesn't equal protecti
Security vendors are playing you for fools, and they're getting rich doing it. Every week I watch UK business owners waste £20,000 on "comprehensive cybersecurity platforms" when they needed £5,000 of basic IT security. The industry deliberately muddies the difference between InfoSec, CyberSec, and IT Security because confused customers pay premium prices for inappropriate solutions. Meanwhile, 50% of small businesses were breached in 2025, proving that expensive confusion doesn't equal protecti
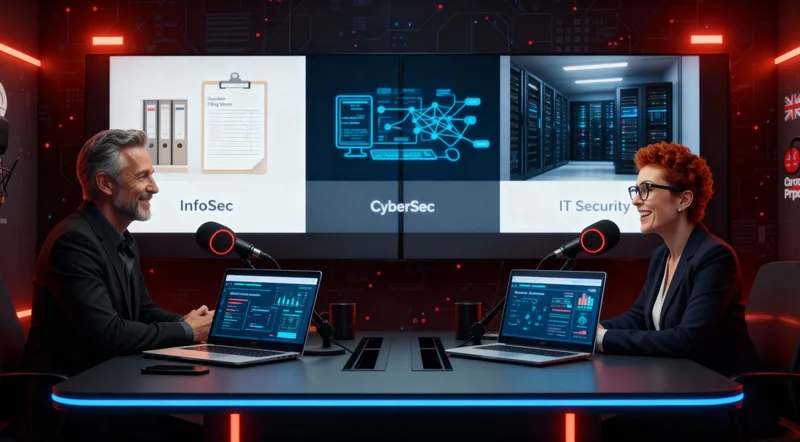
Every week I talk to UK business owners who've just spent £20,000 on "comprehensive cybersecurity platforms" when they needed £5,000 worth of basic IT security. Or they've paid consultants to develop "enterprise information security frameworks" for 15-person companies that can't keep Windows updated. The security industry profits from keeping you confused about InfoSec versus CyberSec versus IT Security. This week's episode cuts through the bollocks to explain what each term actually means, what
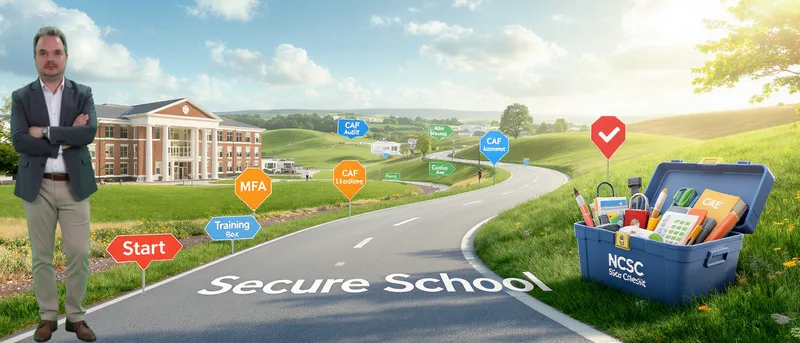
Schools don't need expensive enterprise solutions to improve cybersecurity - they need practical, accessible guidance. The NCSC Cyber Assessment Framework provides exactly that: free, non-technical guidance designed specifically for schools with limited budgets. It covers user access control, incident management, and supply chain security in accessible language. Start with quick wins: enable MFA for everyone, conduct a GitHub repository audit, rotate all credentials organization-wide. The CAF is
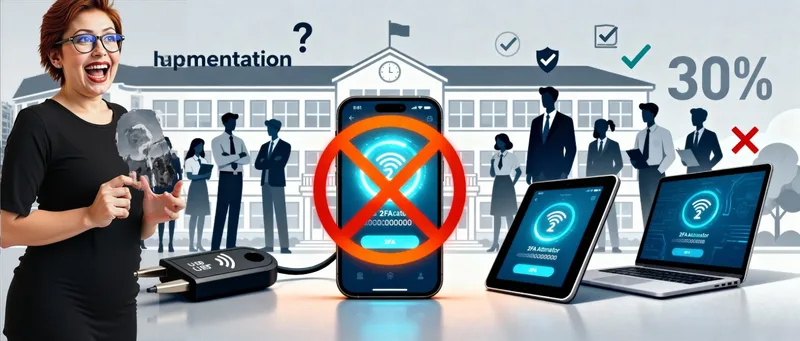
Only 30% of schools have Multi-Factor Authentication enabled, but the reality is worse than that statistic suggests. Many schools have "partial MFA" - enabled for head teachers and SENCOs but not teaching assistants or admin staff. From a security perspective, everyone with access needs MFA, or you're not protected. The challenge? Phone-based authenticator apps conflict with safeguarding policies that ban phones near children. Hardware security keys offer the solution. FIDO2-certified tokens fro
September 1st, 2025 marked a fundamental shift in UK education: cybersecurity officially became a safeguarding issue under the Keeping Children Safe in Education guidance. Paragraph 144 explicitly links cyber security to safeguarding responsibilities, meaning schools can no longer dismiss security as "just an IT problem." This changes everything from a compliance perspective. When framed as "keeping children safe" rather than "good IT security," schools respond differently. Governors now have st
When the Chancellor, three Cabinet Ministers, the NCSC CEO, and the Director General of the National Crime Agency personally co-sign a letter to UK business leaders, you don't ignore it. The NCSC just reported 204 nationally significant cyber incidents, with 18 highly significant attacks marking a 50% increase for the third consecutive year. Marks & Spencer lost over £300 million. A healthcare attack contributed to a patient death. Empty shelves appeared in supermarkets. The government has g
The Kido nursery breach exposed 8,000 children's data in September 2025, but the attack vector reveals a critical lesson for schools: this wasn't sophisticated hacking. Security researchers discovered a publicly accessible GitHub repository containing API credentials in plain text. The kido-kidssafe/myskio-api repository had the "keys to the kingdom visible in the clear." Two 17-year-olds were arrested in Hertfordshire, but the real story is how preventable this breach was. Schools must audit th
This is the complete insider threat action plan for small businesses. Start with the non negotiables. Enable MFA on email and cloud apps. Audit who has access to what. Test your backups and prove you can restore. Then build. Roll out a password manager. Separate admin from day to day accounts. Turn on activity alerts and review them weekly. Segment guest, IoT and finance. Add EDR. Finish with drills, metrics, and monthly reviews. Do your leaders model the right behaviour? Do people know who to c
A teenager extorted 2.85 million dollars from PowerSchool. A student in Iowa ran a grade change business with pocket keyloggers. UK schools lost days of teaching to ransomware. None of this needed elite tools. It needed access, weak controls, and time. That is your wake up call. Do you know what your vendors hold about you? Do you keep more data than you need? Could someone walk up and plug in a device? Layer simple controls. Use MFA. Limit access. Monitor for odd activity. Test restores. Plan f
Small businesses do not need theory. They need controls that block real attacks without new headcount. Start with MFA. It is included in Microsoft 365 and Google Workspace. It kills password reuse and shoulder surfing. Apply least privilege. Split admin from day to day use. Roll out a business password manager. Turn on sign in alerts that flag odd times and places. Test backups with the 3 2 1 rule and keep one copy offline. Segment guest, IoT and finance. These steps are cheap and proven. Will y
Curiosity, access, and a careless password shaped my career. At sixteen I learned the simplest attack works best. I watched a teacher type admin123! and saw the whole network open up. No exploits. Just human nature. That is the insider threat in plain sight. People bypass clumsy controls to get work done. Do your policies help or hinder? Make secure the easy path with least privilege, SSO, MFA, logging, and coaching. Treat incidents as data, not drama. Channel curiosity before it goes undergroun