Enough theory. Today we're getting practical. Whether or not director liability becomes law, demonstrating reasonable care protects your business now. Insurance claims require evidence. Contracts demand due diligence. Regulators ask what you did before the breach. This guide gives you exactly what you need: the five controls that matter, documentation templates, evidence gathering processes, and realistic timelines for businesses of every size. No enterprise consultants required. No massive budg
After two days discussing frameworks and technical standards, let's examine why personal accountability actually works when corporate fines consistently fail. The psychology is fascinating and explains decades of regulatory success and failure. When British Airways faced a £20 million fine, nobody lost their job. When HSE prosecutes directors, workplace safety transforms overnight. The difference isn't the amount of money. It's whose money gets spent and whose freedom gets threatened. Human psyc
Yesterday's podcast proposed criminal liability for cybersecurity negligence. Today, we're dismantling the three-tier framework piece by piece so you know exactly where your business stands. Tier One protects small businesses with explicit gross negligence thresholds and Cyber Essentials safe harbour. Tier Two raises the bar for medium organisations whilst maintaining proportionate standards. Tier Three brings genuine consequences for large enterprises and public sector bodies that still can't i
Yes, you read that correctly. Prison time for directors who allow catastrophic cybersecurity failures. Before you close this tab in horror, hear me out. We already send directors to prison for health and safety failures. Workplace fatalities dropped 85% after the Health and Safety Executive got proper enforcement powers. The ICO? They send sternly worded letters whilst breaches affecting millions go unpunished. Today, Mauven and I lay out exactly what a proper UK cybersecurity enforcement regime
This week, we established why directors should face criminal prosecution for gross cybersecurity negligence. We examined the Synnovis case where a patient died because free MFA was not enabled. We provided technical analysis, psychological examination, and practical implementation guides. Saturday's opinion piece argued forcefully for criminal liability. Next week, we move from "why" to "how." What would a Corporate Cyber Negligence Act actually say? What are the thresholds between bad luck and
I am tired of watching preventable disasters kill people while executives walk away with bonuses intact. A patient died because Synnovis did not enable free multi-factor authentication. Nobody will face criminal prosecution. If a construction director failed to provide hard hats and a worker died, that director would go to prison. Yet when healthcare executives fail to enable free security controls and a patient dies, nothing happens. This is not justice. This is not accountability. This is a br
On 3 June 2024, the Qilin ransomware gang compromised Synnovis, a pathology provider serving NHS hospitals across southeast London. Blood testing collapsed. Over 10,000 appointments were cancelled. More than 1,700 operations were postponed. A patient died waiting for test results that never arrived. The attack succeeded because multi-factor authentication was not enabled. Here is the complete timeline of how a preventable security failure cascaded into catastrophic harm, the technical details of
After this week's coverage of the Synnovis death, many of you have asked: "How do I actually implement MFA in my business?" Here is your complete, practical guide. No jargon, no theory, just step-by-step instructions for enabling multi-factor authentication across your entire organisation. This afternoon. Right now. Whether you are running Microsoft 365, Google Workspace, or a mix of different services, this guide walks you through the exact process. I will show you how to configure systems, dep
Nobody wakes up and decides to let patients die through cybersecurity negligence. Yet that is precisely what happened at Synnovis. The executives who failed to enable multi-factor authentication were not cartoon villains. They were educated professionals running a critical healthcare organisation. So why did they make a decision that, in hindsight, seems obviously catastrophic? The answer lies in the psychological mechanisms that allow intelligent people to rationalise terrible choices, the orga
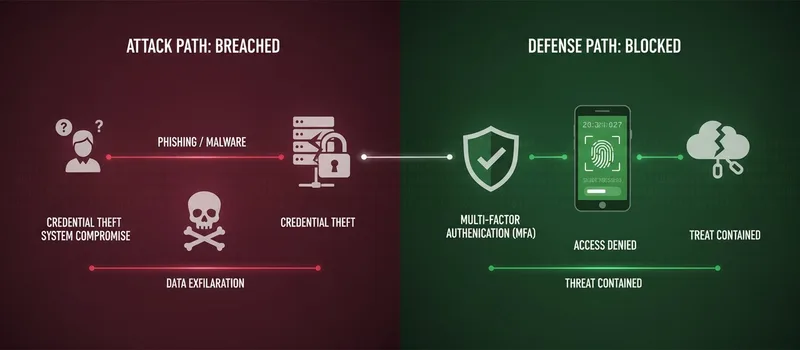
When Beverley Bryant, former Chief Digital Information Officer at Guy's and St Thomas' NHS Foundation Trust, stated that the Synnovis attack "may not have happened" with two-factor authentication enabled, she was not speculating. She was describing technical reality. The Qilin ransomware gang gained initial access through compromised credentials. Multi-factor authentication completely blocks this attack vector. A patient died because a free security control was not enabled. This is not hindsight
On 3 June 2024, a patient arrived at a London hospital A&E feeling unwell. A blood test was ordered. The patient waited. The medics waited. They all waited some more. The patient died. Why? Ransomware had shut down blood testing at Synnovis, the NHS pathology provider. The security control that would have stopped it? Multi-factor authentication. Completely free. Built into every platform. The consequences for executives who chose not to enable it? Nothing. In this episode, we ask the uncomfo
Financial Accountant magazine just published my analysis of the £1.9 billion Jaguar Land Rover cyberattack. But here’s what the article couldn’t cover: the small suppliers who died from JLR’s breach. You didn’t get hacked. Your biggest customer did. You still lost everything. One supplier laid off 40 people because JLR couldn’t place orders for six weeks. Proper security. Good practices. Still went bust. After 40 years in the IT world Intel, Disney, and the BBC, I’ve seen this pattern before. En
Four zero-days. One perfect 10.0 severity score. Hundreds of thousands of sites already compromised. Criminals are exploiting Exchange Servers, Magento shops, and Oracle ERP systems right now - whilst you're reading this. SAP's vulnerability was so bad they deleted the entire component rather than fix it. WordPress sites are falling to a plugin bug that shouldn't exist. And that's just November. Your patching strategy just became a lot more urgent. Graham Falkner breaks down what to patch first:
Ofcom admits it is monitoring VPN use across Britain with a secret AI tool and unnamed data sources. That should worry any small business that relies on encrypted links for daily work. The tool cannot tell a secure office connection from someone dodging age checks. Section 121 still sits in law, ready to force scanning of encrypted chats. Does that sound like a free internet to you? Document your use. Keep your controls tight. Ask your MP why this is acceptable. Do you want regulators watching y
Here's a question for your weekend: Did anyone ask if UK small businesses wanted to fund Microsoft's nuclear reactor restart? Because that's what's happening. While Microsoft spends $1.6 billion restarting Three Mile Island, Google partners with Kairos Power for small modular reactors, and Amazon secures nuclear capacity across multiple projects, your cloud bills are climbing to pay for it. Nobody took a vote. Nobody asked permission. Tech giants made a collective decision that AI is worth unlim
Twenty-three employees. Eighteen months. Forty-seven thousand pounds wasted on cloud infrastructure they didn't need, SaaS subscriptions nobody used, and auto-scaling rules designed by a consultant who'd never checked back. This isn't a horror story about a massive enterprise with unlimited budget. This is CloudBridge Digital, a Nottingham digital agency that discovered they'd been hemorrhaging cash while Microsoft, AWS, and a parade of SaaS vendors quietly helped themselves to the company bank
Microsoft's restarting Three Mile Island. Google's building small modular reactors. Amazon's buying nuclear capacity. And you're getting the bill. While tech giants scramble for gigawatts to power their AI fantasies, your cloud costs are climbing faster than a hyperactive squirrel on espresso. AWS up 15%, Azure up 12%, SaaS tools adding "AI features" you didn't ask for at 20% premium. But here's what nobody's telling you: you don't need to accept this as inevitable. Seven specific actions you ca
Three Mile Island. You remember it, right? The 1979 nuclear accident that terrified an entire generation and effectively killed nuclear power plant construction in America for 40 years? Microsoft just spent $1.6 billion to restart Unit 1. Not for clean energy virtue signaling. Because they're bloody desperate. Google committed to 500 megawatts of Small Modular Reactors. Amazon's all-in on multiple nuclear projects. Meta wants up to 4 gigawatts. Billions in nuclear investment. Timeline: 2028 to 2
They're growing brain tissue in Swiss laboratories and using it to process information. Not simulations. Actual living human neurons, derived from skin cells, housed in specialized chambers, connected to electrodes, computing. FinalSpark's Neuroplatform has 16 brain organoids containing roughly 160,000 neurons total. Each organoid interfaces with 8 electrodes sampling at 30 kHz. The system has operated continuously for four years, testing over 1,000 organoids, collecting 18 terabytes of data. Th
The April 2026 Cyber Essentials update introduces a game-changing rule: multi-factor authentication is now mandatory. Not recommended. Not "nice to have." Mandatory. If your cloud service offers MFA (free or paid) and you're not using it, you automatically fail. No exceptions. This single change will expose how many UK businesses have been skating by with terrible security. With potentially 30,000+ certified companies lacking proper MFA configuration, the fallout will be significant. You've got