March 2024: UK manufacturing company with £18 million turnover lost £2.4 million to business email compromise. Finance director phished, email credentials stolen (no MFA), attacker monitored for two weeks, sent fraudulent payment instruction from compromised account, major client processed payment overseas. Total immediate costs £3.337 million. Company survived through private equity investment that diluted family ownership from 100% to 23%. Managing director resigned. Eight redundancies. What w
Create your first cyber risk register in 2 hours. No consultant needed. Step 1: Identify five specific risks (phishing, ransomware, insider threats are mandatory for all UK SMEs). Step 2: Assess likelihood using real government statistics (85% phishing, 43% breach rate). Step 3: Document impact including business closure potential (28% of SMEs). Step 4: List current controls with verification dates. Step 5: Calculate residual risk scores. Step 6: Specify additional controls with costs. Step 7: A
Why do intelligent board members hear "43% of UK businesses got breached" and think "that won't happen to us"? It's not stupidity; it's psychology. Optimism bias makes us believe bad things happen to others. Present bias makes tomorrow's disaster less urgent than today's deadline. Availability heuristic makes personal experience trump statistics. Illusion of control makes certificates feel like protection. Normalcy bias treats "it hasn't happened yet" as evidence. Dunning-Kruger creates confiden
Most cyber risk registers are useless compliance documents. They contain vague descriptions, unverifiable controls, and no honest assessment of likelihood or impact. A working risk register has exactly seven columns: specific risk scenarios, likelihood based on real UK statistics, quantified impacts including business closure potential, verifiable current controls, residual risk ratings, costed additional controls, and named board-level owners. Every UK SME must address five mandatory risks: phi
Apple released iOS 26.2 on 12 December 2025 patching two WebKit zero-day vulnerabilities that were actively exploited before patches existed. Google's Threat Analysis Group discovered CVE-2025-43529 and CVE-2025-14174 being used in sophisticated attacks against targeted individuals. These vulnerabilities allow arbitrary code execution through malicious websites with no user interaction required. The update patches over 20 vulnerabilities total, including a kernel bug allowing root access and an
Graham Falkner told me before recording that small businesses don't need formal cyber risk registers. By the end of Episode 31, he'd completely changed his mind. UK government data shows only 27% of businesses have board-level cyber security responsibility, down from 38% in 2021. Meanwhile, 43% got breached and 28% of SMEs say a single attack could put them out of business. The evidence is overwhelming. Risk registers aren't bureaucracy - they're systematic thinking applied to survival. This epi
Right, I'm done being diplomatic about this. After 40 years watching the same preventable disasters repeat themselves with different technology, I'm calling it: selling network-connected devices with default administrative credentials should be illegal in the UK. Not "discouraged." Not "recommended against." Illegal. With criminal penalties for manufacturers and civil liability for distributors. Pull up a chair. This intervention has been brewing for three decades. The free market has had 30 yea
A 30-person marketing agency in Manchester did everything right. £15,000 invested in proper security: new firewalls, enterprise endpoint protection, hardware authentication keys for every staff member, and even an external security audit that came back clean. They were feeling quite good about themselves. Two months later? Someone had been accessing their client files for weeks through their HP printer that still used admin/admin as credentials. Total costs: £43,400 direct expenses, three lost c
The ICO just fined LastPass £1,228,283 for security failures. Yes, a password manager company, fined for password security failures. The irony would be funny if 1.6 million UK customers hadn't had their data compromised. LastPass allowed senior employees to access corporate vaults from personal devices and let them link business and personal accounts with one master password. When an attacker exploited vulnerable Plex software on an engineer's home computer, they grabbed the keys to everything.
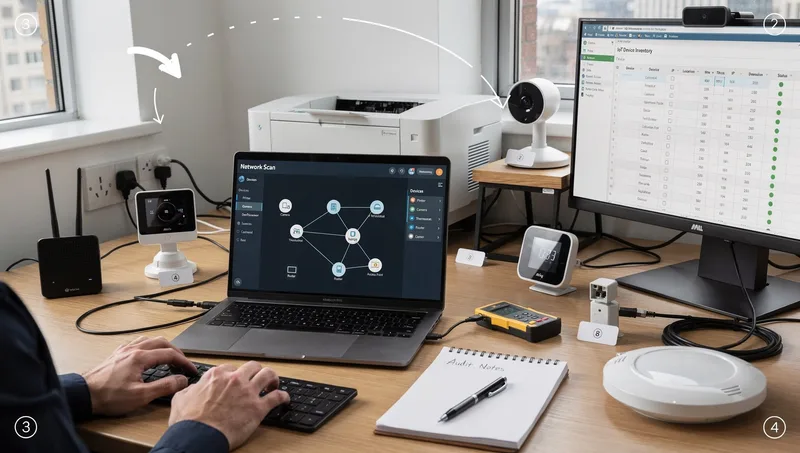
Practical Value: After Monday's podcast about the marketing agency breach through an unsecured printer, the most common question we've received is: "How do I actually do this audit myself?" Fair question. Telling business owners they have a problem is easy. Providing practical steps to fix it is harder. This guide walks you through conducting a comprehensive IoT device audit using free tools. Time investment: 4-6 hours for initial audit. Cost: Free to £200 for network scanning tools. Difficulty:
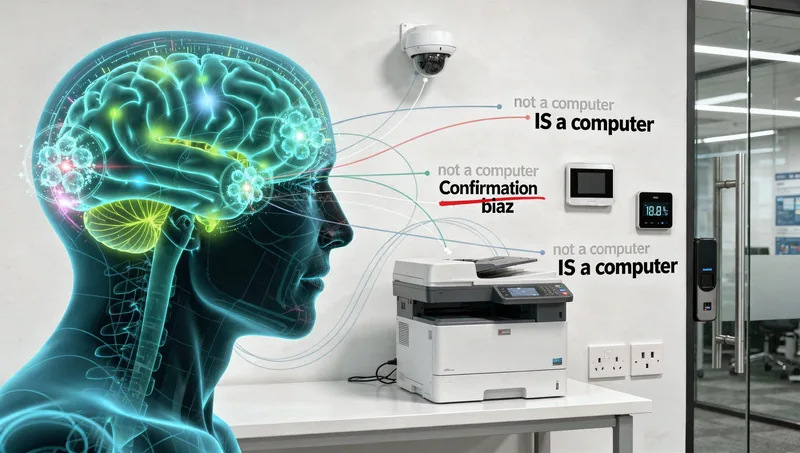
After this week's podcast revelation about the marketing agency losing client files through an unsecured printer, my inbox has been full of variations on the same question: how do intelligent business owners with otherwise solid security miss something this obvious? The answer isn't comfortable, but it's important: IoT security failures aren't about lack of intelligence. They're about systematic psychological blind spots that affect everyone from small business owners to government departments.
December 2025 Patch Tuesday is supposed to be the quiet cruise into Christmas, right? Instead we got fifty seven vulnerabilities, three zero days and one actively exploited Windows privilege escalation that hits almost every supported build. Add in one hundred and thirty nine Adobe fixes and an awkward five week gap until the next Patch Tuesday in January and you have a perfect festive storm. Are you really happy to leave servers and laptops unpatched while everyone is on holiday, or do you want
Right, let's talk about the £15,000 security investment that just got absolutely destroyed by a £300 office printer. A marketing agency did everything right: new firewalls, endpoint protection, hardware authentication keys for every staff member, security audit came back clean. Two months later? Someone had been accessing their client files for weeks through their HP printer still using admin/admin as credentials. While you've been securing laptops and servers, your printer has full network acce
What if I told you the biggest cyber threat to your business isn't hackers, but your office printer? Sounds mad, right? That's what a 30-person marketing agency thought before someone accessed their client files for weeks through an HP printer with factory default credentials. Episode 30 reveals the devices everyone forgets are computers: printers storing documents, CCTV systems livestreaming your premises, thermostats providing network access. Currently Top 12 in Apple Podcasts Management categ
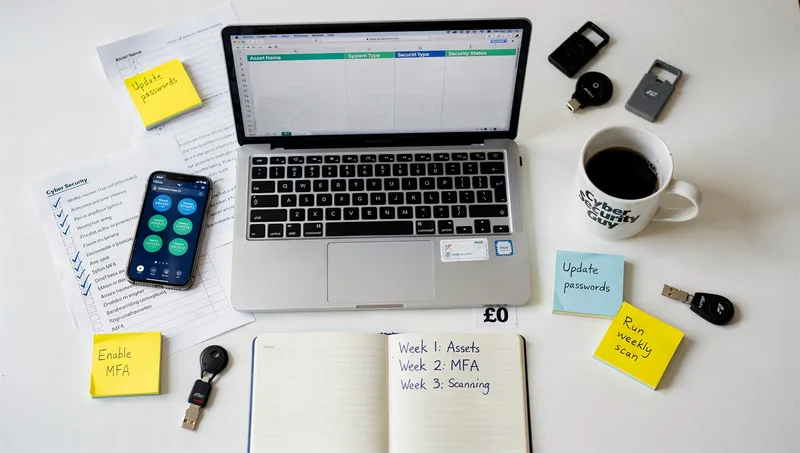
Right, enough theory. Today we're getting practical: the actual tools, templates, and processes you need to implement reverse benchmarking without spending a fortune. Everything in this guide is either free or costs less than a decent takeaway curry per month. Because I'm sick of "enterprise security" guides that assume unlimited budgets and dedicated staff. This is the real-world, shoestring-budget, one-person-wearing-multiple-hats implementation guide. Asset inventory using Google Sheets: free
Noel spent Monday and Tuesday explaining what reverse benchmarking is and how to implement it technically. Both excellent. Both necessary. Both completely inadequate if you don't understand why organizations systematically fail to learn from disasters. Here's the uncomfortable truth: most breaches happen not because organisations don't know what to do, but because human psychology actively prevents them from doing it. Normalcy bias makes us believe disasters happen to others. Optimism bias creat
86 security professionals including former CISA director published advice last year claiming public WiFi, QR codes, and USB charging stations are safe. Sounds credible, except I've spent the year mopping up after businesses who followed exactly this advice. £47,000 stolen via hotel WiFi. Companies breached via QR code phishing. Legal practice ransomwared through compromised charging station. When security elite operate in enterprise bubbles with unlimited budgets, their advice becomes dangerous
Most people copy what the big players do and call it a cyber strategy. That works for them. It probably kills you. This episode flips the script. Instead of worshipping best practice, we dissect the car crashes. Target, Equifax, Colonial Pipeline and SolarWinds. We ask one question. What actually went wrong and have you quietly made the same mistakes in your own business. If you run a UK small or mid sized firm and feel lost in security buzzwords, this is your shortcut. Learn from other peoples
Let's drop the diplomatic language for a moment. Current UK cybersecurity regulation is a comfortable lie we tell ourselves to avoid uncomfortable truths. We pretend fines deter when they don't. We pretend guidance works when it doesn't. We pretend breaches are inevitable when most are preventable. Meanwhile, millions of citizens have their data compromised by organisations that face no meaningful consequences. The Synnovis attack contributed to patient deaths. The ICO's response? Under investig
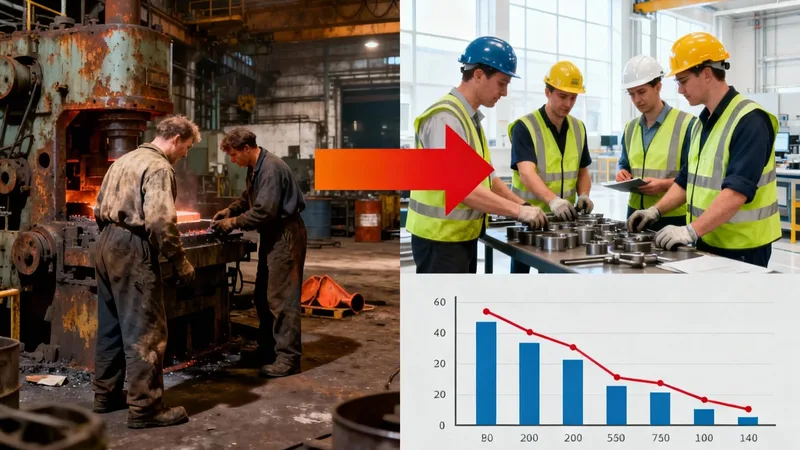
Numbers don't lie. In 1981, 495 workers died in British workplaces. The most recent figures show 124. That's not technological progress alone. That's regulatory teeth. When the Health and Safety Executive gained proper enforcement powers, directors discovered that ignoring safety had personal consequences. Prosecutions made headlines. Behaviour changed. Industries transformed. Today, we examine exactly how HSE enforcement worked and exactly what similar cybersecurity enforcement could achieve. T