The Kido International ransomware attack represents cybersecurity's darkest moment. Eight thousand children's photos, addresses, medical records, and safeguarding notes were stolen and posted online by the Radiant gang. Hackers then called parents directly, demanding they pressure the nursery to pay. This wasn't just a data breach, it was a calculated attack on the most vulnerable data imaginable. After 40 years in cybersecurity, this crosses every line. But here's the terrifying truth: the same
Security fails when it fights how people work. Most breaches are not villains. They are good staff blocked by bad design. The ICO shows students guessed weak passwords or read them off notes. The lesson is simple. If the secure path is slow, people route around it. Make secure the easy choice. Use single sign on. Use MFA that is one tap. Give safe tools for sharing files. Build trust so people report mistakes. Review real behaviour, not policy fantasy. Do your controls help work or hinder it? If
Insider threats are not shadowy hackers. They are people already inside your walls. The ICO found students caused most school data breaches by guessing weak passwords or reading them off sticky notes. They were not breaking in. They were logging in. Sound familiar? If a teenager can bypass controls, what would a bored employee try next? Audit access today. Turn on multi factor authentication. Stop forcing impossible passwords people write down. Log activity on sensitive systems. Train for curios
Enough theory. Time for action. Here's your step-by-step plan to move from "Dave does everything" to sustainable IT support that won't collapse when Dave finally reaches breaking point. Start tomorrow.
You don't need to choose between Dave and professional IT support. The best approach? Dave becomes your strategic IT leader while specialist MSPs handle the complex stuff Dave shouldn't have to figure out alone.
Dave's the only one who knows the admin passwords. Dave's the only one who understands the custom configurations. Dave's the only one who knows which cables do what. When Dave goes, that knowledge disappears. Forever.
After yesterday's Kido International ransomware attack, I've spent the night reading through the technical details and regulatory implications. What I'm seeing isn't just disturbing. It's a fundamental shift in how we need to think about protecting sensitive data in British small businesses. Yesterday morning, 18 UK nursery locations woke up to a ransomware attack. The attackers didn't just encrypt systems. They stole the entire database. Names of 8,000 children. Home addresses. Photos. Safeguar
Co-op's CEO has officially confirmed their April 2024 cyberattack cost £80 million in earnings impact. The perpetrators? Teenagers using basic social engineering to steal personal data from all 6.5 million members. No sophisticated nation-state attack, just "Can you reset my password, mate?" targeting the right employee. With zero cyber insurance coverage, Co-op absorbed every penny while 2,300 stores suffered empty shelves and 800 funeral homes reverted to paper-based systems. But £80 million m
Dave's first in, last out every day. Dave hasn't taken a proper lunch break in months. Dave gets defensive when you ask about the systems. Sound familiar? Your IT manager is drowning, and you've been pretending not to notice
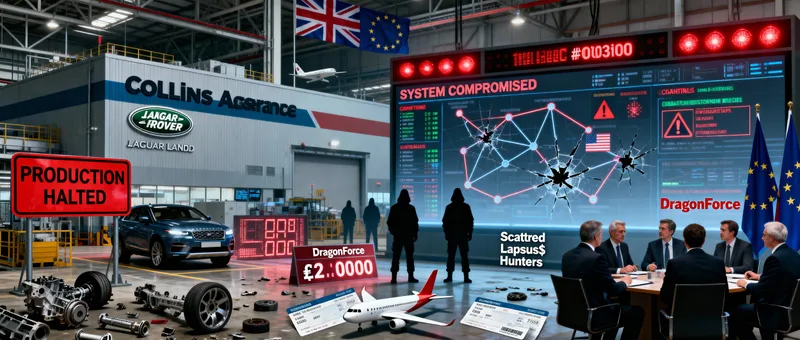
September 2025's Collins Aerospace and JLR cyberattacks weren't just operational disasters - they triggered Europe's first cross-border regulatory crisis under DORA. While aviation experts focused on flight delays, they missed the real story: EU authorities now have direct oversight powers over US companies like Collins Aerospace serving European financial infrastructure. DORA's January 2025 implementation created unprecedented cross-border enforcement mechanisms that most businesses don't under
Let's examine the data: 30 years of single IT manager failures. The patterns are consistent, the outcomes predictable, and the business impact devastating. Here's what happens when your "Dave from IT" model reaches its inevitable breaking point.
You want a network admin, security expert, help desk manager, systems architect, IT consultant, cloud specialist, compliance officer, and data protection expert. For £50k. Are you having a laugh? Here's what you're actually asking for.
September 2025 delivered the most devastating supply chain cyberattacks in UK history. Jaguar Land Rover's £72 million daily losses and Collins Aerospace's airport chaos weren't isolated incidents - they exposed systematic vulnerabilities destroying British business resilience. The same criminal networks using identical social engineering tactics have paralyzed critical infrastructure worth billions. While government offers reactive support, these attacks validate every cybersecurity warning ign
It's Monday morning. Your server's having a wobble. Your email's down. Half your team can't access the customer database. And where's Dave? Probably fixing Janet's printer. Again. Welcome to the single point of failure that's about to snap and take your business with it.
Manchester marketing agency hemorrhaged £800 monthly on cloud storage chaos. Four different platforms, zero coordination, Dave from IT drowning in strategic decisions while fixing printers. Classic small business approach: solve today's problem with today's solution. Six months after engaging fractional CIO services: single integrated platform costing £450 monthly, unified data governance, actual strategic roadmap. Annual savings of £4,200 paid for strategic guidance while delivering competitive
Most UK businesses think they're fine without strategic IT leadership until they're not. These five diagnostic questions expose the difference between thriving with technology and merely surviving despite it. Question 1: Are technology decisions made strategically or reactively? If you're replacing servers because they died rather than planned refresh cycles, you need help. Question 5: Will current systems scale gracefully as you grow? Planning to double in size without considering technology im
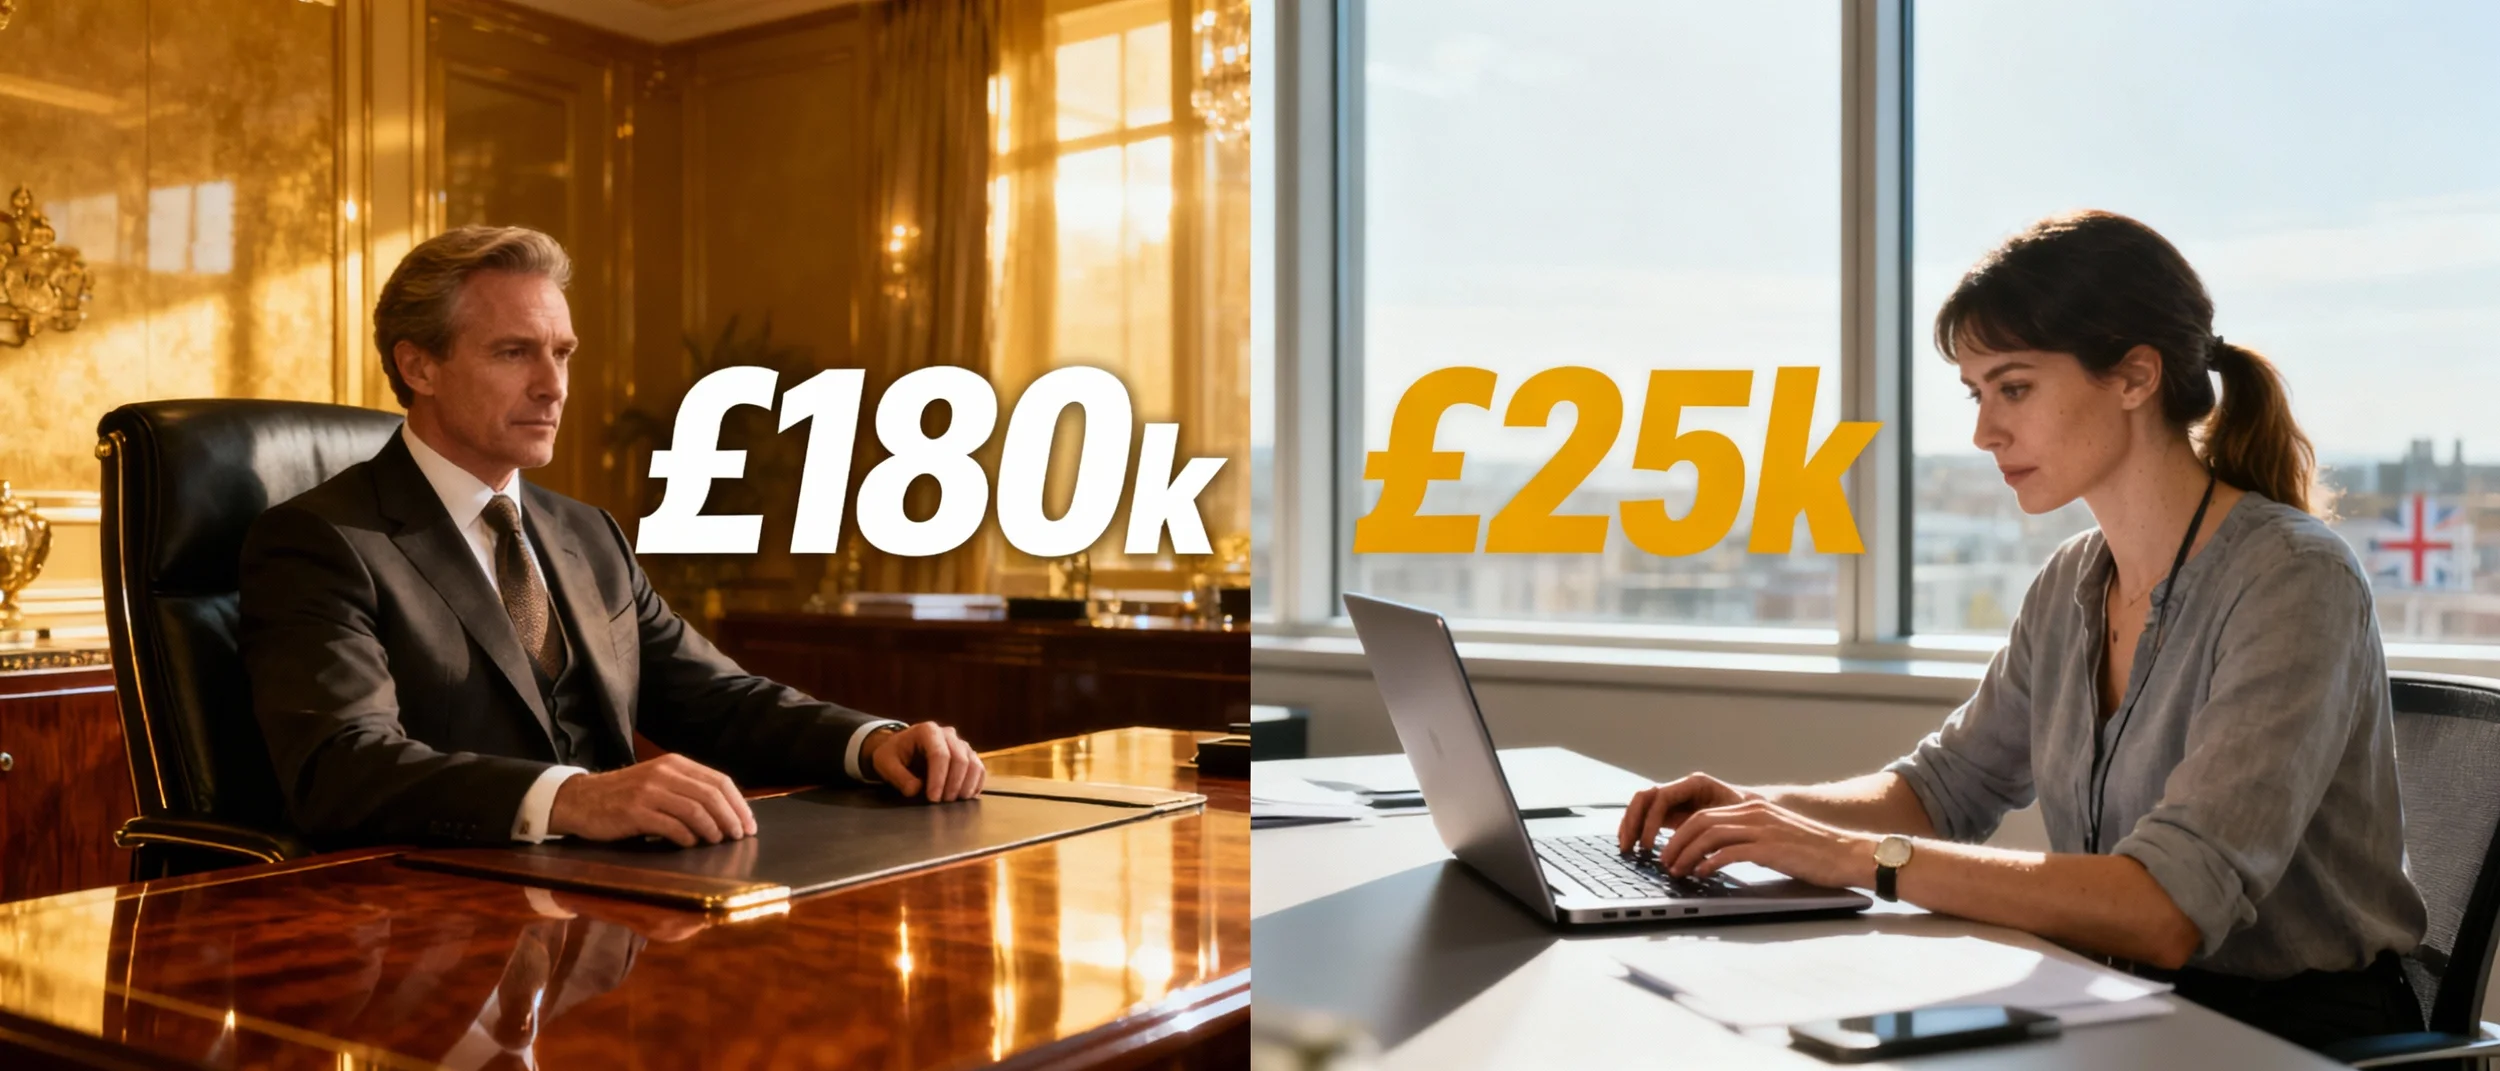
Full-time CIO in London: £180k-250k annually plus benefits. Fractional CIO: £15k-30k for strategic expertise when you need it. The mathematics are brutal, but the quality difference might surprise you. Many fractional executives are senior professionals who prefer variety over corporate politics. You get FTSE 250 CIO experience for a fraction of full-time cost. While your competitors burn budget on executives who spend half their time in meetings, you access strategic guidance scaled to actual n
Dave from IT is brilliant at keeping your systems running. But calling him your CIO is like calling your mechanic an automotive engineer. Most UK small businesses confuse operational IT support with strategic technology leadership, and it's costing them millions. While Dave troubleshoots email issues, real CIOs design five-year technology roadmaps. The difference? Strategic thinking that aligns technology investments with business objectives. Fractional CIO services deliver genuine C-level exper
Cybersecurity isn’t just an enterprise issue — it’s a survival issue for UK SMEs. With 96% of attacks aimed at small businesses and 60% of victims closing within six months, the myth of being “too small to hack” is lethal. This article tears apart the excuses business owners use, reveals the hidden costs of breaches, and explains why simple, affordable defences like Cyber Essentials, patching, MFA, and staff training are the only reason some firms survive. Don’t wait until it’s too late — find o
September’s Microsoft Patch Tuesday isn't just another routine update cycle. With 81 vulnerabilities patched including 9 critical flaws, and active exploitation campaigns already targeting SharePoint servers, this represents significant business risk. Cyber Essentials certified organisations have until September 23rd to deploy updates, but waiting 14 days significantly increases risk exposure. The psychological tendency to defer technical updates creates dangerous security gaps. From authenticat